The 2027 Guide to BNM RMiT Compliance for Next.js Banking Apps
Published by: Gautham Krishna RSep 30, 2026Blog
The Regulatory Shift Nobody Could Ignore
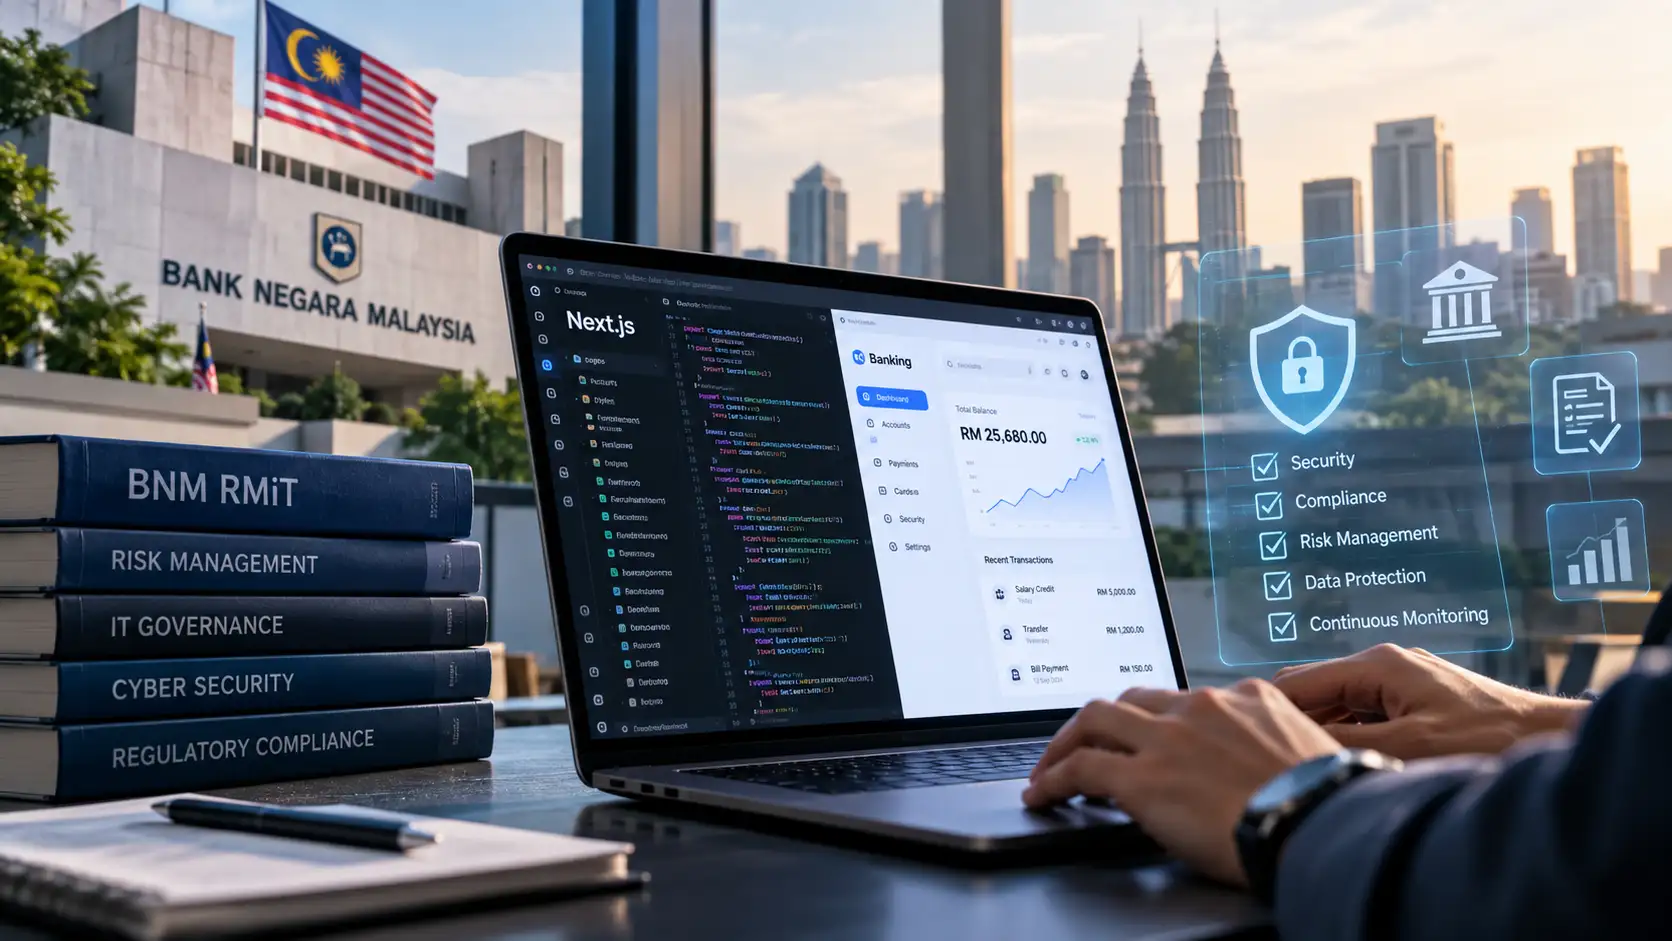
Something fundamental changed in Malaysian financial technology regulation on 28 November 2025. Bank Negara Malaysia issued a revised Risk Management in Technology (RMiT) policy document that replaces the June 2023 version, effective immediately on that same date. This wasn't a cosmetic update. The revised RMiT expands applicability to non-bank Merchant Acquirers and Intermediary Remittance Institutions with significant market share, introduces prescriptive time-bound obligations for resilience and recovery, and mandates cyber supply chain controls including Software Bill of Materials (SBOM) adoption.
For technology teams building banking applications on Next.js, the question is no longer whether the framework can support RMiT-related requirements. It's about understanding exactly where framework capabilities end and where application-level controls, testing practices, and organizational governance begin.
Let's walk through this practically.
Why Next.js Banking Apps Are Everywhere (and What That Means for Risk)
Next.js has become the default choice for financial institutions building modern digital banking interfaces. Its server-first architecture, with Server Components rendering on the server and Server Actions executing mutations server-side, aligns naturally with banking security principles that prioritize minimizing client-side exposure.
But this architectural alignment doesn't translate automatically into RMiT readiness. The framework provides the tooling. The application of that tooling to meet regulatory expectations is an engineering and governance responsibility.
As Capco's 2026 analysis observed, institutions are now assessed not on the existence of governance frameworks but on their practical ability to demonstrate operational resilience, recovery effectiveness, and sustainable technology risk management. The revised RMiT pushes for deeper accountability, broader coverage, and stronger resilience.
The Compliance Flow: From Regulatory Requirement to Evidence
Understanding RMiT compliance for a Next.js banking application means tracing a clear path:
RMiT requirement > Technology risk > Next.js/application control > Testing or validation > Compliance evidence
This isn't theoretical. Here's how it works in practice across the key areas RMiT emphasizes.
The November 2025 RMiT revision converts long-standing authentication guidance into enforceable requirements. Financial institutions must now implement phishing-resistant, device-bound authentication methods. Passkeys (FIDO2/WebAuthn) satisfy phishing-resistant MFA, passwordless authentication, and device binding requirements simultaneously. Transaction-bound MFA, where authentication is tied to specific beneficiary and amount details, is now expected.
Technology risk: Credential theft, session hijacking, phishing attacks targeting banking customers.
Next.js/application control: Next.js 16's App Router architecture supports secure session management through HTTP-only cookies, preventing JavaScript access and mitigating XSS-based session theft. The OWASP Next.js Security Cheat Sheet emphasizes placing authorization close to the data source rather than relying on routing or UI checks. This means implementing a server-only Data Access Layer (DAL) that performs authorization and returns minimal Data Transfer Objects.
Testing and validation: Authentication flows must be tested by calling server entry points directly, without using the user interface, as the OWASP guidance recommends. This catches authorization bypasses that UI-level testing misses.
Compliance evidence: Authentication architecture documentation, penetration test results demonstrating phishing resistance, and session management test reports.
Role-Based Access Control and API Security
RMiT requires appropriate access controls for identification and authorization of users accessing financial systems. For Next.js applications, this creates specific challenges because the framework has multiple server entry points -- Server Actions, Route Handlers, Server Components -- and a check in one does not protect another independently callable path.
Technology risk: Privilege escalation, unauthorized access to customer data, API endpoint exploitation.
Next.js/application control: Treat every Server Action as a client-callable POST entry point requiring authentication and resource authorization. Route Handlers must be treated as HTTP endpoints with explicit audiences. Layout-level authorization does not protect independently callable descendants.
Testing and validation: API security testing should verify that every entry point enforces authorization independently. Input validation using runtime schemas (Zod or similar) is mandatory -- TypeScript is not validation.
Compliance evidence: API security test reports, authorization matrix documentation, input validation coverage reports.
Performance, Availability, and Resilience
The revised RMiT introduces prescriptive time-bound obligations for capacity planning and degradation detection. Financial institutions must conduct proactive capacity planning that factors in peak loads and projected growth, implement early-warning systems to detect service degradation, and establish stand-in processing capability by 30 September 2027 for least-substitutable services.
Technology risk: Service outages during peak transaction periods, cascading failures from IT interdependencies, customer harm from prolonged disruptions.
Next.js/application control: Next.js supports streaming server rendering and incremental static regeneration, which can contribute to graceful degradation strategies. Server Components can be designed to fail independently without taking down the entire application.
Testing and validation: Performance testing must simulate peak loads and degradation scenarios. Resilience testing should validate that the application behaves correctly under partial failure conditions.
Compliance evidence: Capacity planning documentation, performance test results under peak load, degradation detection system logs.
Logging, Monitoring, and Incident Detection
The revised RMiT expands cybersecurity expectations to include Security Operations Centre capabilities, cyber operations readiness, and continuous monitoring. Financial institutions must demonstrate sufficient audit trails and monitoring of anomalous transactions.
Technology risk: Undetected breaches, delayed incident response, inability to reconstruct security events.
Next.js/application control: Next.js applications should implement structured logging for authentication events, authorization failures, and suspicious activities. Server-side logging captures events that client-side monitoring would miss.
Testing and validation: Incident detection testing should validate that monitoring systems actually detect simulated attacks, not just that logging is configured.
Compliance evidence: Monitoring coverage reports, incident detection test results, audit trail samples.
Dependency and Patch Management
The revised RMiT introduces SBOM requirements for continuous vulnerability monitoring and secure open-source software practices. This directly affects Next.js applications, which depend on hundreds of npm packages.
Technology risk: Supply chain attacks, exploitation of known vulnerabilities in dependencies.
Next.js/application control: Automated dependency scanning, SBOM generation for every build, and patch management processes. The Next.js framework itself must be kept current -- historical vulnerabilities in framework versions demonstrate the importance of timely updates.
Testing and validation: Vulnerability scanning should be integrated into CI/CD pipelines, with automated blocking of builds containing critical vulnerabilities.
Compliance evidence: SBOM artifacts, vulnerability scan reports, patch management logs.
The Testing Layer That Makes Compliance Verifiable
RMiT compliance isn't achieved through configuration alone. It requires demonstrable evidence that controls work as intended.
Recent enforcement actions reveal that regulators are scrutinizing operational resilience, recovery effectiveness, and technology risk management with increasing rigor. Institutions have been penalized for prolonged disruptions affecting online banking and digital services beyond acceptable recovery thresholds, as well as failures in incident response execution.
For Next.js banking applications, this means testing must cover:
Security testing: Penetration testing of authentication flows, authorization bypass attempts, injection attacks, and API endpoint security.
QA automation: End-to-end testing of critical user journeys -- login, fund transfers, account management -- with automated regression suites that catch security regressions.
Performance testing: Load testing under realistic peak conditions, stress testing to identify breaking points, and resilience testing to validate degradation behavior.
API testing: Validation of every endpoint's authentication, authorization, input validation, and rate limiting.
This is where specialized expertise becomes essential. Evalogical's security testing and QA automation services are designed for exactly this kind of regulatory-driven testing challenge. Their approach integrates automated testing into DevSecOps pipelines, providing the continuous validation evidence that RMiT readiness requires.
Third-Party Integrations and the Supply Chain Gap
The revised RMiT mandates due diligence on all service providers and subcontractors, continuous monitoring of vendor risk including cybersecurity posture, and enforcement of SLAs requiring immediate disclosure of incidents and remediation timelines.
For Next.js banking applications, third-party integrations include payment gateways, identity providers, cloud services, and open-source libraries. Each represents a potential supply chain vulnerability.
The practical response involves implementing SBOM tooling, establishing open-source security policies covering repository access and secure coding practices, and reviewing SLAs to include disclosure and resilience clauses by Q2 2026.
Data Protection and Disaster Recovery
RMiT requires effective measures to address data accessibility, confidentiality, integrity, sovereignty, recoverability, and regulatory compliance. For Next.js applications processing customer financial data, this translates to encryption in transit and at rest, proper key management, and data residency controls.
Disaster recovery planning must account for the application's dependencies -- database systems, authentication providers, API gateways, and third-party services. The revised RMiT emphasizes annual cyber exercises, CERT readiness, out-of-band communications, and recovery testing.
Every RMiT-related control must have corresponding evidence. This isn't about generating paperwork -- it's about maintaining a living record that demonstrates controls are functioning.
For Next.js applications, the evidence trail includes:
- Architecture documentation showing security boundaries
- Authentication and authorization test reports
- API security assessment results
- Performance and resilience test reports
- SBOM artifacts and vulnerability scan results
- Monitoring and incident detection test records
- Patch management logs
- Third-party due diligence records
This documentation serves both regulatory examination and internal governance. As PwC's December 2025 analysis noted, the revised RMiT enables organisations to move from compliance-based oversight to proactive, risk-informed resilience.
The Malaysian financial sector faces an average of one million cyber-attack attempts daily, according to BNM. Most are blocked, but the volume and sophistication continue to increase. In 2025 alone, Malaysians lost RM2.8 billion to scams, and financial institutions prevented RM1.19 billion in fraudulent transactions -- a threefold increase from the previous year.
These numbers underscore why RMiT compliance isn't a checkbox exercise. It's an ongoing operational discipline.
For teams building Next.js banking applications, the path forward involves embedding security throughout the development lifecycle, automating testing to generate continuous evidence, and maintaining the documentation that demonstrates resilience. Evalogical's digital transformation and application modernization capabilities support financial institutions in building these practices into their engineering culture rather than treating compliance as an afterthought.
Frequently Asked Questions
Q. Is Next.js itself RMiT compliant?
A. No. Next.js is a framework, not a compliance solution. RMiT compliance is an organizational responsibility that involves governance, technology controls, testing practices, and documentation. Next.js provides capabilities that can support compliance efforts -- such as server-first architecture and secure session management -- but using Next.js does not make an application compliant. Each institution must evaluate its specific implementation against applicable RMiT controls.
Q. What are the key changes in the November 2025 RMiT revision?
A. The revised RMiT expands applicability to non-bank Merchant Acquirers and Intermediary Remittance Institutions with more than 5% market share, introduces prescriptive time-bound obligations for capacity planning and degradation detection, mandates SBOM adoption for supply chain risk management, and converts authentication guidance into enforceable requirements for phishing-resistant, device-bound methods.
Q. How does RMiT affect authentication for banking applications?
A. The revised RMiT requires phishing-resistant, transaction-bound authentication methods. SMS OTP is effectively being moved away from as the industry shifts toward passkeys (FIDO2/WebAuthn), device binding, adaptive MFA, and risk-based authentication. Authentication must also be bound to specific transaction details including beneficiary and amount.
Q. What testing evidence does RMiT compliance require?
A. Testing evidence includes penetration test results, authentication and authorization test reports, API security assessments, performance and resilience test results, vulnerability scan reports, and incident detection test records. The emphasis is on demonstrable evidence that controls function as intended, not just that they exist.
Q. What is the deadline for stand-in processing capability?
A. The revised RMiT requires financial institutions to establish stand-in processing capability for least-substitutable services by 30 September 2027, with fraud controls in place.
Q. How should Next.js applications handle authorization to support RMiT requirements?
A. Authorization should be placed close to the data source using a server-only Data Access Layer, not relying on routing or UI checks. Every server entry point -- Server Actions, Route Handlers, Server Components -- must enforce authorization independently because a check in one does not protect another. Testing should validate authorization by calling entry points directly, without the UI.
Ready to Build Compliance-Ready Banking Applications?
The regulatory landscape for Malaysian financial technology is evolving faster than most engineering teams can track. Building Next.js applications that support RMiT requirements demands more than framework knowledge it requires security testing expertise, QA automation, and a deep understanding of how regulatory expectations translate into technical controls.
Explore Evalogical's banking and financial services solutions to see how their software development, QA automation, security testing, and application modernization capabilities can support your compliance readiness journey. Whether you're modernizing legacy systems or building new digital banking experiences, the right testing and security practices make all the difference.

 AI-Powered Account Planning: T....
 How AI-powered follow-ups help....
 How AI-powered account briefs ....
 How AI-powered CRM updates tur....
 Turning Customer Signals Into ....

Your Trusted Software Development Company